
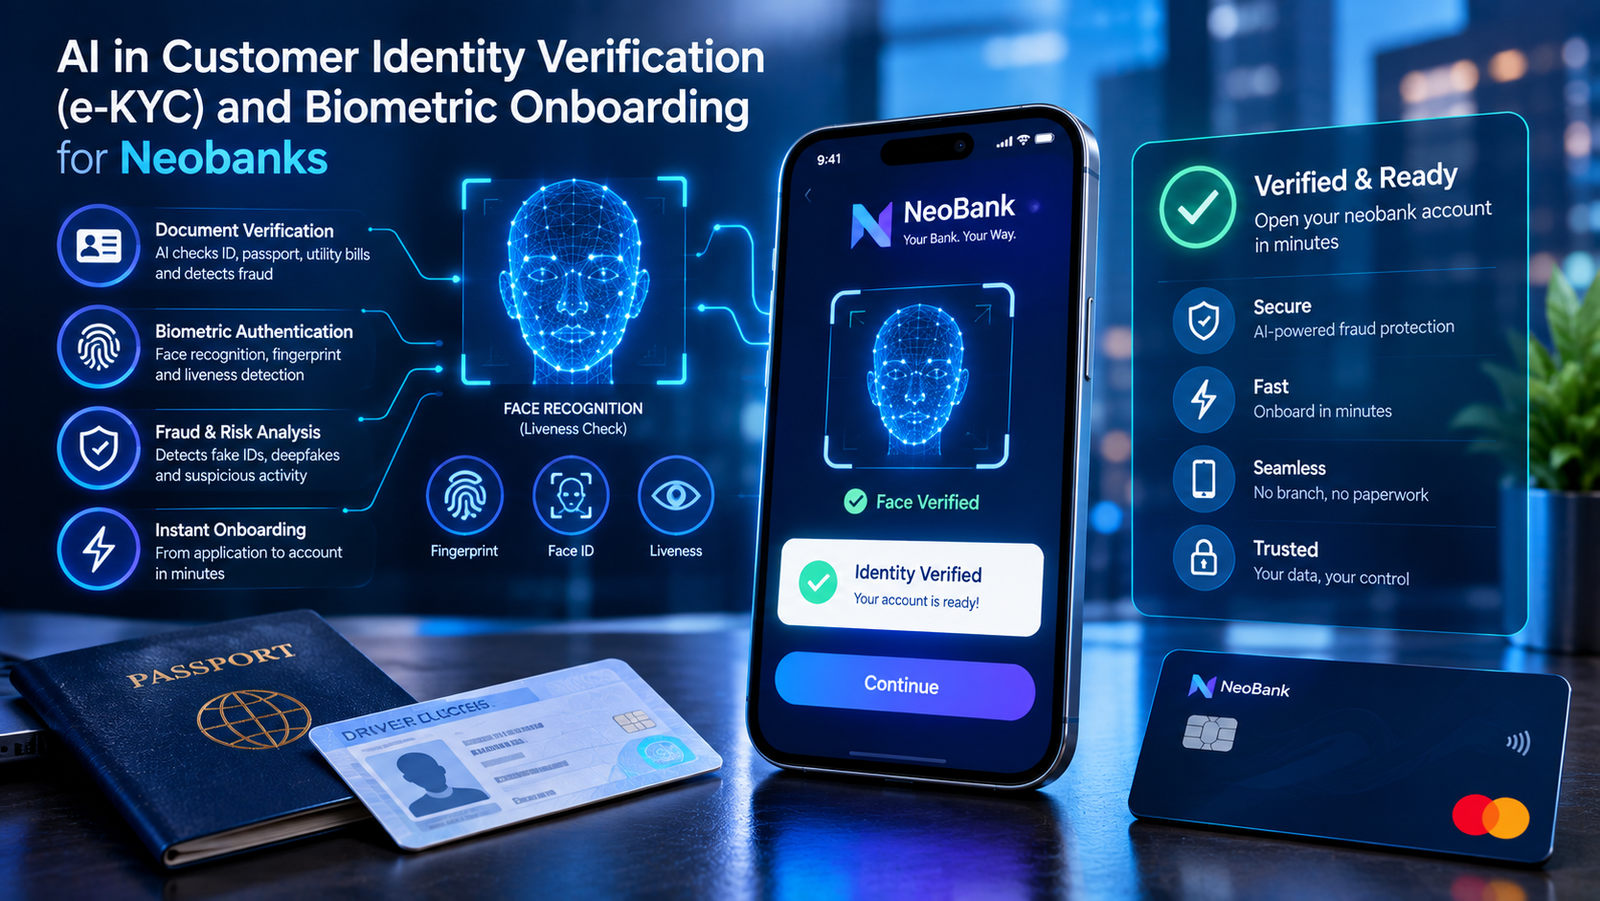
Primary topic: AI in Customer Identity Verification (e-KYC) and Biometric Onboarding for Neobanks
Research focus: AI-powered identity verification, document intelligence, facial biometrics, liveness detection, deepfake prevention, synthetic identity fraud, onboarding risk assessment, customer experience, privacy, model fairness and regulatory compliance
Why AI-Powered e-KYC Matters for Neobanks
Neobanks deliver banking services primarily through digital channels. Customers may open an account, submit identity documents, complete a selfie check and receive an onboarding decision without visiting a branch. This model can reduce the friction associated with traditional account opening, but it also removes many of the face-to-face checks that banks have historically used to establish identity.
Electronic Know Your Customer, or e-KYC, is the digital process used to collect and verify customer identity information. Depending on the jurisdiction and the product, it may include identity-document checks, biometric verification, database checks, address verification, sanctions screening and risk-based due diligence.
AI can automate parts of this process, but it should not be treated as a replacement for the bank’s complete KYC obligations. A face match does not establish that a document is genuine, that the person is not using a synthetic identity, or that the customer presents an acceptable financial crime risk. Each check answers a different question.
Identity assurance
Does the evidence support the identity the applicant claims?
Fraud prevention
Does the application show signs of impersonation or manipulation?
Customer experience
Can a genuine customer complete onboarding without unnecessary friction?
Compliance
Can the bank explain, evidence and audit its verification decisions?
The most useful AI architecture treats these as connected but separate objectives. A system optimized only for fraud detection may reject too many genuine applicants, while a system optimized only for conversion may allow avoidable fraud.
How AI-Based Biometric Onboarding Works
A modern onboarding workflow usually combines several AI and non-AI controls. The exact sequence depends on the bank’s risk appetite, customer segment, available identity infrastructure and regulatory requirements.
Personal details and consent
Image quality, document type and OCR
Layout, security features and data consistency
Face comparison and liveness / presentation-attack detection
Duplicate identity, fraud signals and required screening
When all required checks pass
Request additional evidence
Resolve uncertainty or risk
This workflow should not be designed as a single pass-or-fail model. A document may be readable but suspicious, a face match may be strong while liveness is uncertain, or a genuine applicant may have a poor camera or an expired document. Separate signals help the bank choose an appropriate next step instead of rejecting every application that does not fit the ideal path.
Research Evidence: What the Studies Tell Us
Digital onboarding process mining: detecting fraud through user journeys
A study published in *Computers* examined identity fraud in online banking onboarding using process mining and a real fintech event log. Instead of looking only at the information submitted by an applicant, the researchers examined the sequence of actions taken during the onboarding process. Process mining reconstructs how users move through a digital workflow, allowing analysts to identify patterns that differ between legitimate and fraudulent applications.
The study reported approximately **80% accuracy** for machine-learning classifiers that distinguished fraudulent from legitimate users in the studied dataset. It also used process discovery to create a visual representation of the onboarding process. The finding is relevant because fraud may be reflected in how an application is completed, not just in the document or face image supplied by the customer.
For a neobank, behavioral process signals might include repeated attempts, unusual navigation sequences, inconsistent device changes or multiple applications following a similar pattern. These signals should be treated as investigation clues rather than proof of fraud. The reported accuracy is specific to the study’s data and setup, and should not be assumed to represent performance in a different bank or country.
Source: Using Process Mining to Reduce Fraud in Digital Onboarding, Computers
What this means for product teams
Capture onboarding events in a structured, privacy-conscious way. Use process analytics to discover where fraud attempts cluster, where genuine users struggle and which steps create avoidable abandonment.
NIST face recognition evaluation: demographic differences matter
The U.S. National Institute of Standards and Technology (NIST) evaluated face recognition algorithms in its Face Recognition Vendor Test programme. Its demographic-effects research examined how false-positive and false-negative rates vary across age, sex and racial groups. The evaluation covered a large collection of algorithms and image datasets, and found demographic differentials in the majority of the algorithms studied.
This matters directly to biometric onboarding. A false match may allow an impostor to pass a verification step, while a false non-match may prevent a genuine customer from opening an account. The impact is therefore two-sided: errors can create security exposure and unfairly exclude legitimate users.
NIST also explains that image quality can affect performance. Poor lighting, under-exposure, over-exposure and camera angle can increase the chance that two images of the same person are not matched. These are practical concerns for mobile onboarding, where customers use different devices, cameras and environments.
The lesson is not that facial verification should be abandoned. It is that a neobank must evaluate the exact system it deploys, under realistic capture conditions, and examine performance across relevant demographic groups.
Source: NIST, Face Recognition Vendor Test Part 3: Demographic Effects
Additional source: NIST Face Recognition Technology Evaluation, Demographic Effects
NIST digital identity guidelines: biometric verification needs safeguards
NIST’s Digital Identity Guidelines, SP 800-63-4, provide a detailed framework for identity proofing and authentication. The guidelines address biometric accuracy, presentation-attack detection, demographic performance, consent, retention and alternative methods.
For remote identity proofing, the guidelines specify presentation-attack detection requirements for biometric capture. They also set performance expectations for one-to-one biometric verification and require attention to demographic impacts. Where one-to-many biometric identification is used for deduplication or fraud detection, the guidance calls for manual review before declining enrollment based on an automated match.
These requirements are valuable for neobanks because biometric onboarding involves more than comparing two face images. The system must establish that the sample comes from the applicant, protect against spoofing and avoid treating an uncertain automated result as definitive evidence.
NIST is a standards and guidance source rather than a controlled trial of a particular neobank product. Its value is in translating identity assurance principles into measurable requirements that financial institutions can use when selecting and validating vendors.
Source: NIST SP 800-63-4, Identity Proofing Requirements
Related guidance: NIST SP 800-63B, Authentication and Authenticator Management
Responsible AI in financial identity verification: security is not the only outcome
A 2026 review, *Responsible AI in Financial Identity Verification and Risk Mitigation*, examines AI use in KYC, biometric and document verification, machine-learning fraud detection and the governance challenges surrounding financial identity systems.
The review identifies three recurring themes. First, biometric and behavioral methods combined with anomaly detection can improve detection capabilities compared with relying only on traditional rules. Second, these gains are accompanied by concerns about explainability, demographic bias and the governance of data across jurisdictions. Third, differences between regulatory environments make deployment more difficult for financial institutions operating internationally.
For neobanks, this is a reminder that a technically effective verification model can still be unsuitable if customers cannot understand the process, decisions cannot be audited, or biometric data is handled without appropriate controls. Model performance, customer experience, privacy and regulatory compliance need to be assessed together.
Because this is a narrative literature review, its conclusions synthesize prior research rather than reporting one universal benchmark for all e-KYC systems.
AI and deepfake detection in financial video-KYC
A 2026 paper in *Forensics and AI* examines deepfake detection in financial video-KYC systems. It explores a privacy-preserving approach that combines micro-expression analysis with multimodal metadata, including signals from video and the capture environment. The paper addresses a key limitation of systems that depend on a single facial or visual signal: synthetic media and manipulated inputs can target the specific assumptions on which that signal relies.
For neobanks, this research points toward layered liveness checks rather than a simple instruction to blink or turn the head. A robust system may combine facial motion, image consistency, device and capture signals, and checks designed to detect injection attacks. The model should also be tested against realistic attack methods and poor-quality devices.
The paper’s proposed approach should be understood as research into a detection architecture, not proof that deepfake attacks can be eliminated. Attackers adapt, and the results of a research system need independent validation before production use.
AI-powered financial fraud detection: organizational readiness affects results
A 2026 study in *Humanities and Social Sciences Communications* examined how AI-based financial fraud detection is implemented in Pakistan’s banking sector. It combined a systematic literature review with interviews involving banking professionals and customers. The research found that the effectiveness of AI depends not only on technical capability but also on staff understanding, organizational readiness, workforce skills and governance.
Although the study covers financial fraud detection more broadly rather than e-KYC alone, its implementation findings are relevant to neobanks. An identity verification model cannot deliver its intended value if operations teams do not understand its alerts, escalation processes are unclear or model decisions cannot be translated into action.
The study is particularly useful as an implementation lesson: technical deployment should be accompanied by staff training, clear ownership, operational testing and a feedback loop between fraud teams, product teams and engineering.
What These Research Findings Mean Together
The studies point to a more complete way to evaluate e-KYC. Identity verification is not one model and not one metric. It is a chain of decisions in which an error at one stage can affect the entire onboarding outcome.
| Evidence area | Main insight | Practical application |
|---|---|---|
| Process mining | User journey patterns can help identify fraud | Analyze onboarding events and repeated behavior |
| NIST demographic testing | Biometric error rates can differ across groups | Test real-world performance by demographic group |
| NIST identity guidance | Remote biometrics need presentation-attack safeguards | Validate liveness, spoof resistance and fallback paths |
| Responsible AI review | Accuracy must be balanced with explainability and privacy | Maintain governance, audit trails and data controls |
| Deepfake detection | Single visual signals can be attacked | Use layered, multimodal anti-spoofing controls |
| Operational readiness | People and processes affect AI effectiveness | Train teams and define clear escalation ownership |
AI Technologies Used in e-KYC
Document AI and intelligent data extraction
Document AI uses optical character recognition, computer vision and machine learning to extract information from identity documents. It can identify document type, read names and dates, detect missing fields and compare extracted information with data entered by the applicant.
The value is not limited to faster data entry. AI can flag inconsistencies, such as a mismatch between a typed date of birth and the information extracted from a document. Image analysis can also identify signs of alteration, although document authenticity should be assessed using appropriate security features and trusted verification sources rather than a visual model alone.
Facial matching
Facial matching compares a live selfie or video frame with the portrait on an identity document or another trusted reference. The model produces a similarity score, which is evaluated against a defined threshold.
The score should not be treated as a probability that the applicant is honest or that the document is genuine. It answers a narrower question: how similar are the compared biometric samples under the model’s measurement.
Liveness and presentation-attack detection
Liveness systems attempt to determine whether the biometric sample is being presented by a live person rather than a photograph, video replay, mask or other spoof. Modern systems may also need to defend against virtual cameras, injected media and AI-generated video.
A neobank should not rely on a single gesture-based check. It should evaluate the complete capture process, including the trustworthiness of the device and media path, and use additional verification when the result is uncertain.
Behavioral and device risk signals
AI can analyze application behavior, device characteristics and repeated patterns across applications. These signals may help identify automated account creation, coordinated fraud attempts or unusual onboarding sequences.
Such data can be sensitive and may be unreliable when customers use shared devices, privacy tools or assistive technologies. Device and behavioral signals should therefore contribute to a risk assessment rather than automatically determine eligibility.
Visual: The Multi-Layer Identity Assurance Model
Document evidence
Is the identity document readable, consistent and authentic?
Biometric evidence
Does the applicant resemble the reference identity?
Live presence
Is the sample resistant to presentation and injection attacks?
Contextual risk
Does the application show suspicious patterns or conflicting evidence?
Approve, request another check, refer for review or decline according to documented policy
Where Neobanks Can Use AI Beyond Initial Verification
AI-based identity assurance can continue after account opening. The same customer may later change a phone number, reset credentials, add a new payment recipient or request a high-risk transaction. These events may require stronger verification than routine account access.
Useful applications include:
- Detecting duplicate or potentially synthetic identities during onboarding
- Identifying unusual patterns across multiple account applications
- Adding verification when a customer changes sensitive account details
- Supporting account recovery when a device is lost
- Prioritizing cases involving possible impersonation
- Monitoring whether fraud patterns change after a model or vendor update
The key design principle is proportionality. A low-risk action should not trigger the same level of friction as an application with several conflicting signals. Step-up verification can help protect the account without repeatedly asking every customer to complete the full onboarding process.
Comparison: Rules-Based KYC vs AI-Assisted e-KYC
| Capability | Rules-based approach | AI-assisted approach |
|---|---|---|
| Document processing | Fixed templates and field rules | OCR, image analysis and flexible extraction |
| Face verification | May rely on a vendor’s fixed matching workflow | Similarity scoring with quality and risk signals |
| Fraud patterns | Known rules and watchlists | Anomaly detection and pattern discovery |
| Decision explanation | Often straightforward if rules are explicit | Requires model explanations and evidence logs |
| Adaptability | Rules need manual updates | Models can be retrained and monitored, with governance |
AI does not make rules obsolete. Regulatory requirements, sanctions screening and mandatory checks often need explicit, deterministic controls. AI is most useful where the bank needs to interpret images, compare patterns or prioritize uncertain cases.
Major Risks and How to Control Them
| Risk | Why it matters | Control |
|---|---|---|
| Deepfake and injection attacks | Fake media may attempt to bypass remote checks | Layered liveness, trusted capture and attack testing |
| Demographic performance gaps | Some groups may face more false matches or rejections | Independent subgroup testing and remediation |
| Poor capture quality | Lighting, camera quality and document wear affect results | Capture guidance and retry or alternative paths |
| Privacy and biometric retention | Biometric information is sensitive and difficult to replace | Data minimization, access control and deletion policies |
| Vendor dependency | Performance and availability may depend on a third party | Due diligence, service monitoring and fallback vendors |
| Unexplained rejection | Genuine applicants may be blocked without recourse | Manual review, reason codes and appeal process |
Privacy, Consent and Biometric Data Governance
Biometric information deserves stronger protection than ordinary onboarding data. A password can be changed after compromise; a person’s face cannot be replaced in the same way. Neobanks should therefore collect only what is necessary, define how long it is retained and restrict access to staff and vendors who need it.
NIST’s identity-proofing guidance addresses consent, retention, deletion and independent testing of biometric systems. It also emphasizes that biometric information should be treated as sensitive personal information and that customers should have appropriate alternatives where required by the applicable framework.
Practical governance measures include:
- Explain why biometric verification is being requested
- Record consent where required
- Document the purpose and retention period for biometric data
- Encrypt biometric templates and related identity evidence
- Limit access and maintain audit logs
- Assess vendors and subprocessors before sharing data
- Provide an accessible alternative where the legal and risk framework permits it
- Test deletion and retention controls instead of relying only on policy documents
The bank should also distinguish raw images, extracted document data, biometric templates, match scores and investigation records. They may have different retention needs and should not automatically be stored together indefinitely.
Source: NIST SP 800-63-4, Identity Proofing Requirements
Expert Recommendation
Neobanks should procure or build e-KYC as a measurable identity-assurance system, not as a single facial-recognition feature. The most important design decision is to separate evidence collection, verification, risk assessment and final disposition.
A practical recommendation is to begin with a well-defined onboarding journey and establish a baseline before adding more AI. Measure completion rates, manual-review rates, fraud outcomes, false rejections, time to decision and performance across customer groups. Then introduce AI where the evidence shows a specific problem, such as document extraction errors, repeated identity fraud or an excessive manual-review burden.
The bank should also insist that vendors provide more than a headline accuracy figure. Ask for test methodology, attack coverage, demographic performance, operating thresholds, model-update practices, incident reporting, data retention details and evidence from conditions similar to the bank’s actual customer base.
For high-impact decisions, maintain a route for human review. A low-confidence biometric result should generally trigger another appropriate check or review, not an unexplained permanent rejection. Human review must itself be governed, consistent and monitored.
Expert Quote
NIST’s core biometric warning: “Biometric characteristics do not constitute secrets.”
Source: NIST, Digital Identity Guidelines, SP 800-63B
This principle is central to financial onboarding. A face image may be captured, copied or generated, so a biometric match alone cannot establish that the person is present and acting legitimately. Neobanks need presentation-attack detection, trusted capture processes and additional controls around the account.
Source: NIST SP 800-63B, Authentication and Authenticator Management
Implementation Roadmap for a Neobank
Foundation: Map the current onboarding journeyDocument every user step, data field, vendor call, decision rule and manual handoff. Identify where applicants abandon the process and where fraud or identity errors are detected.
Data and controls: Define evidence requirementsSpecify supported identity documents, required checks, biometric consent, retention rules, security controls and acceptable fallback methods for each customer segment.
Pilot: Validate AI components separatelyTest OCR, document authenticity, face matching, liveness and behavioral signals independently before evaluating the complete onboarding workflow.
Controlled launch: Use risk-based routingStart with a limited customer segment. Route uncertain cases to additional checks or trained reviewers, and monitor errors before expanding automated decisions.
Ongoing operations: Monitor and improveTrack fraud outcomes, customer friction, demographic performance, vendor changes and model drift. Revalidate the system after material changes.
KPIs for AI e-KYC and Biometric Onboarding
| KPI | What it measures | Why it matters |
|---|---|---|
| Onboarding completion rate | Share of applicants who finish the process | Shows customer friction |
| Time to decision | Time from application start to outcome | Measures operational speed |
| Manual-review rate | Share routed to human review | Helps plan operations capacity |
| False-match and false-non-match rates | Biometric verification errors | Balances security and access |
| Presentation-attack detection rate | Performance against tested spoof attempts | Measures resistance to impersonation |
| Fraud confirmed after onboarding | Subsequent confirmed identity-related fraud | Tests real-world effectiveness |
| Demographic performance gap | Differences in error rates between groups | Identifies unequal outcomes |
No single KPI should be optimized in isolation. For example, reducing manual review may improve operating cost but increase fraud exposure if the system simply approves more uncertain applications. Similarly, a strict biometric threshold may reduce false matches while increasing false non-matches and customer abandonment.
Future Predictions: 2027–2030
More layered defenses against synthetic identity and deepfake attacks
As synthetic media becomes easier to produce, neobanks are likely to place greater emphasis on combining document, biometric, device and capture-integrity signals. A single selfie check will be less suitable as the sole basis for identity assurance in higher-risk cases.
More adaptive, risk-based onboarding
Onboarding will increasingly adapt to the evidence collected. A straightforward application may pass through a low-friction path, while an application with inconsistent evidence receives a step-up check or manual review. The challenge will be making these paths consistent, explainable and fair.
Greater emphasis on measurable biometric fairness
Financial institutions will face continued pressure to test biometric systems against the population and devices they actually serve. Procurement decisions will increasingly depend on independently evaluated performance, not only vendor claims or aggregate accuracy.
Privacy-preserving identity verification
Neobanks will have stronger incentives to minimize the collection and retention of raw biometric data. Privacy-preserving methods, carefully designed biometric templates and better deletion controls may become more prominent, although their suitability will depend on technical maturity and regulatory requirements.
Identity verification will extend across the customer lifecycle
The same identity-assurance capabilities may be used for account recovery, sensitive profile changes, new-device enrollment and selected high-risk transactions. The future system will be less like a one-time onboarding gate and more like a continuous, risk-based identity service.
These are forward-looking expectations, not guaranteed outcomes. Their pace will depend on attack trends, regulatory requirements, vendor capabilities and the quality of real-world evidence.
Startup and Product Opportunities
AI e-KYC creates opportunities for fintech infrastructure providers, RegTech companies and identity technology startups.
- Document intelligence API for extracting and validating identity documents across supported formats
- Deepfake and injection detection for remote video onboarding
- Biometric quality and fairness monitoring for institutions using third-party verification vendors
- Onboarding fraud analytics that detects repeated patterns across application journeys
- Explainable identity risk engine that combines verification signals into reviewable evidence
- Privacy-aware identity orchestration that minimizes data sharing between onboarding providers
- Manual-review copilot that summarizes evidence and helps investigators resolve uncertain cases
- e-KYC monitoring dashboard for tracking completion, fraud, fairness and vendor performance
A particularly useful product opportunity is an independent e-KYC quality and monitoring layer. Rather than replacing every identity provider, it could help neobanks compare vendors, detect performance drift, measure demographic gaps and document the reasons behind onboarding outcomes.
Frequently Asked Questions
What is AI in e-KYC?
AI in e-KYC uses techniques such as computer vision, OCR, biometric matching, liveness detection and anomaly detection to support digital customer identity verification and onboarding risk assessment.
How does biometric onboarding work in a neobank?
A customer typically submits an identity document and a selfie or video. The system extracts document information, checks the document, compares the face with the reference portrait and tests whether the capture appears to come from a live person. Additional checks may be required before the bank makes an onboarding decision.
Can AI completely prevent deepfake identity fraud?
No. AI can help detect manipulated media and suspicious capture patterns, but no single model can guarantee that every deepfake, injection attack or synthetic identity will be detected. Layered controls and ongoing testing remain necessary.
Why is biometric fairness important?
Differences in false-match and false-non-match rates can affect both security and access. A system that performs poorly for a particular group may expose the bank to risk while making legitimate customers more likely to fail verification.
Should a failed face match automatically reject an applicant?
Not necessarily. Poor lighting, camera quality, document condition or a genuine mismatch can produce an uncertain result. Depending on the bank’s policies and applicable requirements, the next step may be a retry, another verification method or human review.
What is the biggest AI opportunity for neobanks?
One of the strongest opportunities is a risk-based onboarding system that combines document intelligence, biometric verification, liveness detection and application-level fraud signals while keeping decisions explainable and providing appropriate routes for genuine customers who need assistance.
Final Perspective
AI-powered e-KYC can help neobanks make digital account opening faster and more secure, but the strongest systems will not be built around facial recognition alone. They will combine document intelligence, biometric comparison, liveness detection, application-level analytics and risk-based decision-making.
The research supports this broader approach. Digital onboarding process mining shows that user journeys can reveal patterns relevant to fraud detection. NIST’s face recognition evaluations demonstrate why biometric performance must be tested across demographic groups and realistic image conditions. NIST’s digital identity guidelines emphasize presentation-attack safeguards, privacy, retention and alternative methods. Recent research into responsible financial identity verification and deepfake detection further highlights the need for explainability, multimodal defenses and operational validation.
For a neobank, the goal should be to verify identity with confidence while keeping the process accessible to legitimate customers. That requires more than a high accuracy score. It requires reliable evidence, transparent decisions, secure handling of biometric data, a fair customer journey and a clear process for resolving uncertain cases.
The most sustainable architecture is:
Neobanks that treat these components as one governed identity-assurance system will be better positioned to balance onboarding conversion, fraud prevention and customer trust.
Research Sources
- Using Process Mining to Reduce Fraud in Digital Onboarding, Computers
- NIST, Face Recognition Vendor Test Part 3: Demographic Effects
- NIST, Face Recognition Technology Evaluation: Demographic Effects
- NIST SP 800-63-4, Identity Proofing Requirements
- NIST SP 800-63B, Authentication and Authenticator Management
- Responsible AI in Financial Identity Verification and Risk Mitigation, Discover Sustainability, 2026
- Federated Micro-Expression Mining and Multi-Modal Metadata Fusion for Deepfake Fraud Detection in Financial Video-KYC Systems, 2026
- AI-Driven Financial Fraud Detection in Pakistan’s Banking Sector: Bridging Strategic Intent and Operational Implementation, 2026

Leave a Reply