
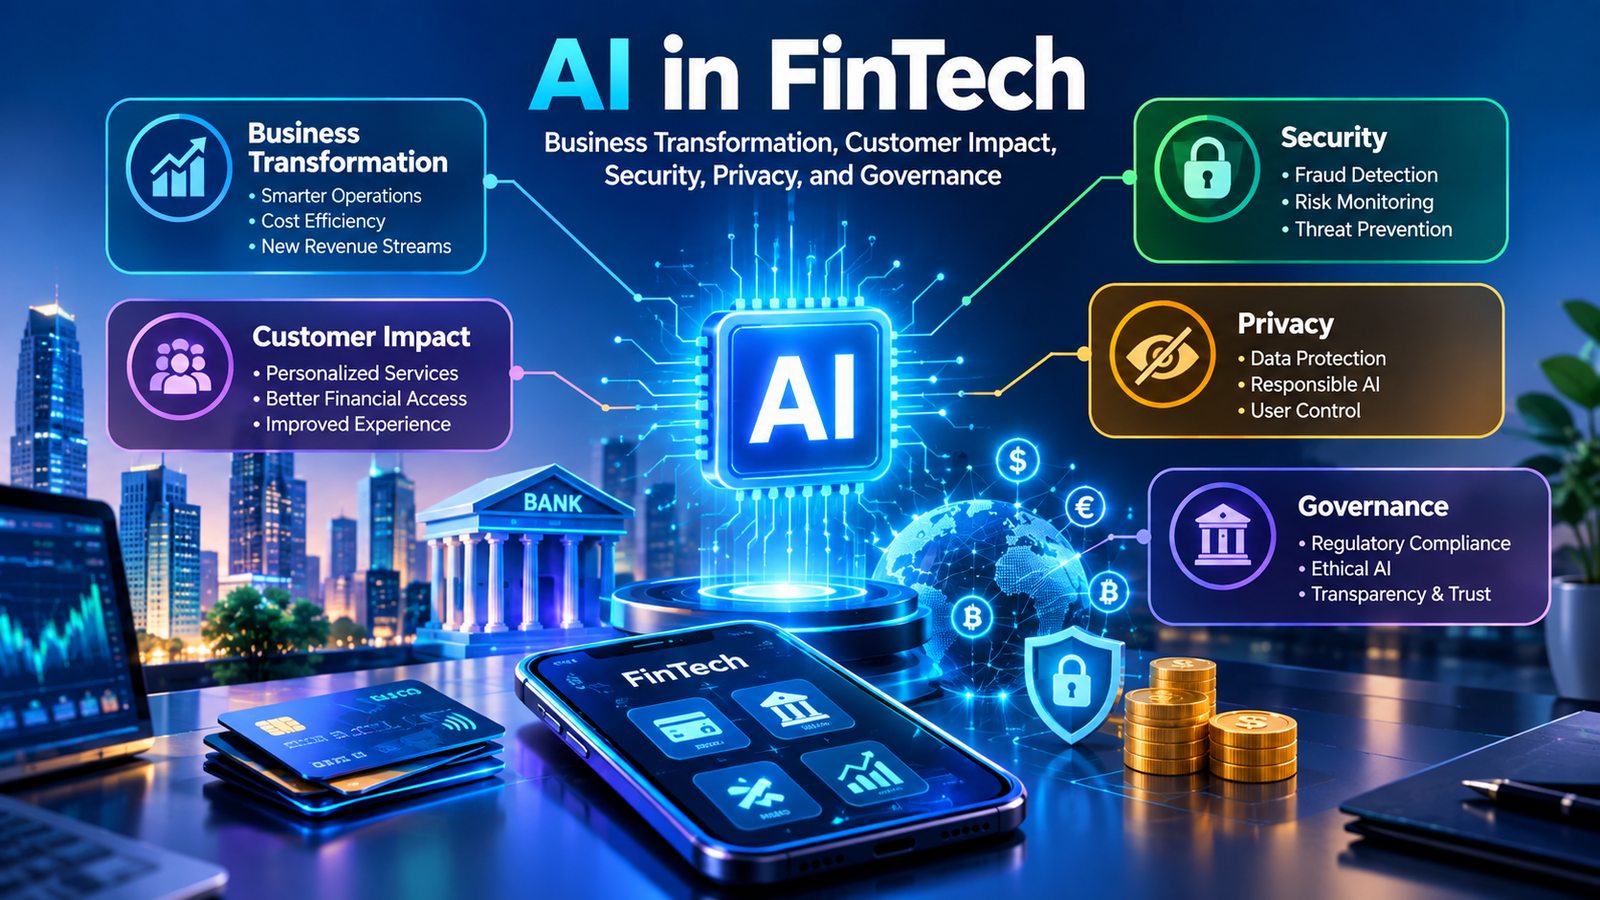
Primary topic: AI in FinTech: Business Transformation, Customer Impact, Security, Privacy, and Governance
Research focus: AI-powered customer experience, credit decisioning, fraud detection, deepfake and synthetic identity risk, KYC vendor security, and the fast-moving global rulebook for AI in financial technology
What “AI in FinTech” Actually Covers
FinTech AI is not one tool. It is four layers stacked on top of each other. Each layer carries a different risk level.
| Layer | What it does | Example |
|---|---|---|
| Customer-facing AI | Talks to users directly | Chatbots, voice assistants, robo-advisors |
| Decisioning AI | Makes or supports a financial decision | Credit scoring, loan approval, BNPL underwriting |
| Trust and safety AI | Verifies identity and blocks fraud | KYC checks, transaction monitoring |
| Agentic back-office AI | Runs multi-step tasks with less human review | Automated compliance workflows, agent-linked payments |
The first two layers are now common. Most fintech apps use them today. The last two layers are newer. They are also where most 2026 security incidents happened.
Visual: How AI Touches a Single Customer Journey
AI reads the ID document
AI checks the selfie and liveness
AI scores credit risk
AI monitors every transaction
AI chatbot answers questions
Five AI touchpoints. Five separate risk points. Each one needs its own control.
The Business Case: Why FinTech Keeps Adding AI
The numbers explain the pace of adoption. Gartner forecasts that AI agents will handle 70 percent of customer interactions in banking by 2026. Forty percent of complex queries will resolve with no human involved. European fintech investment rose 5 percent year over year in the first half of 2026. Funding is on track to grow 18 percent if that pace holds. Fintech Global tracked 1.36 billion dollars in fintech funding across just twelve deals in the first week of September 2026 alone.
The pitch is simple. AI cuts onboarding time. AI cuts support costs. AI catches fraud faster than a human team ever could. That is all true. It is also why the failures below matter so much. A tool this deeply embedded fails at scale, not in isolated cases.
Why Security, Privacy, and Governance Became Urgent in 2026
Three separate incident categories forced this issue onto every fintech board agenda this year.
153 million driver’s licenses exposed from one identity-verification vendor
Deepfakes now make up 6.5 percent of all fraud attempts, up 2,137 percent since 2022
The US, UK, and EU are now writing three different rulebooks for the same AI tools
Incident 1: The IDScan breach exposed the KYC supply chain
In September 2026, identity-verification vendor IDScan.net confirmed a security incident. A dark-web marketplace called Nexus had been advertising more than 153 million stolen US and Canadian driver’s license scans. The data included names, license numbers, and ID document images. Investigative journalist Brian Krebs traced the leak back to IDScan’s cloud infrastructure. Nine class-action lawsuits were filed within three days. The FBI opened a formal investigation. IDScan’s technology sits inside age checks, rental car counters, and online onboarding flows used by many other companies. Its clients did not choose to expose this data. Their vendor did it for them.
This is the core lesson for fintech: your KYC vendor’s security posture is now your security posture.
Incident 2: Deepfake fraud moved from rare to routine
Deloitte research found more than 40 percent of financial professionals have directly encountered deepfakes used in fraud attempts. Ninety percent say fraudsters are actively using generative AI in their operations. In just the first half of 2025, deepfake-related fraud losses passed 410 million dollars, with some single incidents exceeding 680,000 dollars.
Sumsub data shows deepfakes now account for 6.5 percent of all fraud attempts globally. That is a 2,137 percent increase since 2022. North America saw the sharpest jump, with a 3,000 percent rise in deepfake fraud reported by Onfido. Financial services firms are targeted 300 times more often than other industries, according to KnowBe4.
Source: Deepfakes in Financial Services: How AI Fraud Is Reshaping Risks in 2026, Fourthline, and Deepfake Statistics 2026: Growth, Fraud and Detection Data, StationX
Incident 3: Synthetic identities are beating KYC checks by design
Security researchers at the 2026 Deepfake Summit described “KYC validated” bank accounts for sale on dark-web forums, priced at 150 to 200 dollars each. Criminals build these accounts using stolen data combined with an AI-generated persona and fake ID documents. Some fraud rings hold these accounts for years, building real credit history, before cashing out with a large, coordinated default. Panelists noted a blunt reason this keeps working: many fintech startups are measured by account volume. That gives them little financial incentive to slow down and scrutinize new signups closely.
Research Study: Generative AI Can Now Forge Real-Looking ID Documents
A 2026 academic study tested whether generative AI models can create convincing fake identity documents. The answer was yes. The paper cites the Monetary Authority of Singapore’s own analysis, which found deepfakes now affect biometric authentication, targeted social engineering, and corporate digital risk. Financial institutions face five compounding risk types from this: market risk, cyber risk, fraud risk, regulatory risk, and reputational risk, often from a single incident.
What fintech teams can learn:
- Do not treat document upload plus selfie match as sufficient identity proof anymore
- Add liveness detection that checks for synthetic generation artifacts, not just face matching
- Assume a well-resourced attacker can produce a passable fake ID and a matching deepfake selfie
- Layer behavioral and device signals on top of document checks, since documents alone are no longer reliable
Source: Can Generative Models Actually Forge Realistic Identity Documents?, arXiv, 2026
Research Study: KYC Checks Are Losing the Arms Race
Industry research from Fintech Global found that AI-generated fraud is evolving faster than most KYC teams can respond. Compliance staff are hired for judgment. Increasingly, they spend their day doing manual search work instead. The research frames this as a resourcing problem as much as a technology one.
What fintech teams can learn:
- Automate the repetitive search work so compliance staff can focus on judgment calls
- Track detection-to-fraud ratio over time, not just raw fraud-attempt counts
- Expect stricter incident-reporting timelines going forward, since regulators now expect proactive controls
- Move away from one-time onboarding checks toward continuous, behavior-based monitoring
Source: Why Your KYC Checks Are Failing Against AI-Generated Fraud, Fintech Global, September 2026
Research Study: Human Detection of Deepfakes Is Not Good Enough
Research compiled by Eftsure found that human reviewers correctly spot high-quality deepfake video only 24.5 percent of the time. The average financial cost of a deepfake identity fraud case grew from 230,000 dollars in 2022 to 450,000 dollars in 2024. That is a 96 percent increase in two years. Nearly one in three business leaders reported no confidence that their own staff could recognize a deepfake fraud attempt.
What fintech teams can learn:
- Do not rely on staff training alone to catch deepfakes, since even trained humans miss most of them
- Budget for automated deepfake-detection tools as a baseline cost, not an optional upgrade
- Track the dollar cost per fraud incident, not just the count, since average losses are rising fast
- Run internal deepfake-awareness drills the same way you run phishing drills
Source: Deepfake Statistics 2026: Key Facts for CFOs, Eftsure
Research Study: AI Governance Rules Are Fragmenting by Region
A 2026 review by the International Bar Association found that the UK, EU, and US are taking three different approaches to AI in financial services. The UK relies on existing frameworks like the Consumer Duty and Senior Managers regime, rather than new AI-specific law. The EU’s AI Act treats credit scoring as a high-risk use case, with binding compliance duties. The US remains split between federal pull-back and rising state-level activity, following the CFPB’s withdrawal of more than 60 guidance documents in 2025.
What fintech teams can learn:
- Build a compliance program flexible enough to meet the strictest regional rule, then localize down from there
- Track state-level rulemaking closely in the US, since states are filling gaps left by federal pull-back
- Treat credit-scoring AI as high-risk by default if you operate in or sell into the EU
- Revisit your compliance map at least twice a year, since this landscape is still moving fast
What the Experts Are Saying
Turner, AI governance panelist, Zishi financial-services webinar, 2026
Where AI Creates Value Across FinTech
| Function | AI capability | Main risk | Key control |
|---|---|---|---|
| Onboarding | Reads ID documents and verifies liveness | Deepfake and synthetic identity fraud | Multi-signal verification, not document checks alone |
| Credit decisioning | Scores risk and approves or denies credit | Bias and unfair lending outcomes | Explainability and regular fair-lending audits |
| Fraud and AML monitoring | Flags suspicious transactions in real time | False positives and missed novel fraud patterns | Human review before account freezes |
| Customer support | Chatbots resolve routine queries | Wrong or misleading financial guidance | Clear escalation path to a human agent |
| Vendor and third-party AI | Embedded AI inside core banking or lending platforms | You cannot see inside a vendor’s model | Vendor AI risk assessment before signing |
Actionables: What Different Teams Should Do Right Now
Governance is not one team’s job. It needs a different checklist for each group.
For Business Leaders and Executives
- Ask your KYC and identity-verification vendor how it stores document scans, and for how long
- Require a written incident-response plan for any AI vendor before signing a contract
- Fund deepfake-detection tools as a fixed line item in next year’s security budget
- Assign one named owner for AI governance, since “everyone’s job” usually means no one’s job
- Review your regional regulatory exposure at least twice a year
For Developers and Engineers
- Log every AI-driven decision with its input, model version, and output, for audit purposes
- Never let a customer-support AI directly authorize a fund transfer without a hard confirmation step
- Add liveness and injection-attack checks to any onboarding flow that uses a camera or microphone
- Build a kill switch for every AI agent that can touch money, and test it before launch
- Separate AI research environments from production systems that hold live customer data
For Startups and Founders
- Do not measure growth by signup volume alone, since that incentive is exactly what fraud rings exploit
- Budget for identity-fraud losses from day one, not after your first major incident
- Pick KYC vendors with a public security track record, not just the cheapest integration
- Build compliance flexibility into your product from the start, since rules differ by region and change often
- Treat “we use AI for KYC” as a security claim you must be ready to defend, not just a marketing line
For Compliance and Risk Teams
- Move from one-time onboarding checks to continuous, behavior-based monitoring
- Track your detection-to-fraud ratio over time, not just the raw number of blocked attempts
- Map every third-party AI vendor your company depends on, including sub-vendors you cannot directly see
- Run a tabletop exercise simulating a KYC vendor breach before it happens to you
- Keep a live register of which AI systems are classified high-risk under applicable law
Risk Tiers: Matching Oversight to What the AI Can Do
| Tier | Example | Required control |
|---|---|---|
| Assist | Chatbot answers a balance question | Clear labeling that it is an AI, with an escalation path |
| Recommend | AI suggests a credit limit change | Human sign-off and an explainable reason code |
| Execute bounded tasks | AI auto-approves small, low-risk loans | Fixed approval ceiling and regular bias audits |
| High-impact decision | AI freezes an account or denies a large loan | Mandatory human review before the action takes effect |
Implementation Roadmap
List every AI system touching money, identity, or credit decisions
Test one bounded, reversible use case first
Add logging, kill switches, and human review
Reuse the same controls across every new AI feature
KPIs to Track
| KPI | What it tells you |
|---|---|
| Deepfake detection rate | How much fraud your current tools actually catch |
| Average fraud loss per incident | Whether losses are growing even as detection improves |
| Vendor AI risk coverage | Share of third-party AI tools formally assessed |
| Kill-switch response time | How fast you can stop a malfunctioning AI agent |
| Model decision audit coverage | Share of AI decisions with a full, logged reason code |
Future Predictions: 2027 to 2030
2027: Vendor AI Risk Reviews Become Standard Due Diligence
Expect fintechs to demand security audits from every AI vendor before integration, not after an incident like IDScan’s.
2028: Deepfake Detection Becomes a Baseline Feature
Detection tools will stop being a premium add-on. They will become a default part of every onboarding flow, the same way spam filters became default in email.
2029: Continuous Identity Monitoring Replaces One-Time Checks
Static, sign-up-only KYC will look outdated. Expect ongoing, behavior-based identity checks throughout the customer relationship.
2030: Regional AI Rulebooks Converge Around Shared Principles
The US, UK, and EU are unlikely to write identical laws. But expect shared baseline principles, like explainability and human override, to emerge across all three.
Startup and Product Opportunities
- Deepfake-detection API: Screens video and voice in real time during onboarding and support calls
- Vendor AI risk-scoring tool: Rates the security posture of KYC and identity vendors before you sign
- Continuous identity monitoring platform: Replaces one-time KYC checks with ongoing behavioral signals
- AI decision audit trail service: Logs every automated credit or fraud decision for regulators
- Cross-region compliance mapping tool: Tracks which AI use cases are high-risk in which jurisdiction
- Synthetic identity detector: Flags accounts built from a mix of real and AI-generated data
Frequently Asked Questions
Is AI safe to use for fintech customer onboarding?
It can be, but document checks and a selfie match are no longer enough on their own. Add liveness detection and behavioral signals too.
What actually happened in the IDScan breach?
A dark-web marketplace advertised more than 153 million stolen driver’s license scans. Researchers traced the source to identity-verification vendor IDScan.net’s cloud systems.
How much has deepfake fraud actually grown?
Deepfakes now make up 6.5 percent of all fraud attempts. That is a 2,137 percent increase since 2022, according to Sumsub data.
Can humans reliably spot a deepfake?
No. Research shows human reviewers catch high-quality deepfake video only about 24.5 percent of the time.
Which regulator’s AI rules should a fintech follow?
All of them that apply to your markets. The US, UK, and EU currently use different approaches, so multinational fintechs need a flexible compliance program.
What is the single highest-priority fix for most fintechs right now?
Review your KYC and identity-verification vendor’s security practices. That single supply-chain link caused 2026’s largest disclosed identity breach.
Final Perspective
AI has made fintech faster. It has also made fintech a bigger target. The IDScan breach showed that one vendor’s weak security can expose your entire user base. The deepfake fraud numbers show that old verification methods no longer work alone. The regulatory picture shows that governance is now a real cost of doing business, not a side project.
None of this means fintechs should slow down AI adoption. It means every team, from the boardroom to the engineering team, needs its own clear checklist. Build that now. Do not wait for your own incident to force the issue.
For sector-specific playbooks that apply the same governance discipline elsewhere in finance, see our related guides on AI Security and Governance in Banking, AI Security and Governance in Capital Markets, AI Security and Governance in Investment and Asset Management, AI Security and Governance in Insurance, and our earlier guides on AI in Trading: Market Transformation, Algorithmic Risk, Security, and Governance and AI in Crypto: Industry Transformation, Security, Privacy, and Governance.
For deeper coverage of AI-driven fraud and finance topics discussed above, see our earlier reporting on AI in real-time digital wallet fraud detection and prevention, AI in credit scoring and underwriting, AI in alternative credit scoring for underbanked populations, AI in anti-money laundering, and AI in automated micro-lending and instant approval workflows.
Sources
- IDScan Confirms Breach Tied to 153 Million Stolen Driver’s Licenses, eSecurity Planet, September 2026
- The IDScan Data Breach: 153 Million ID Scans Advertised and Nine Class Actions in Three Days, Zyphe, September 2026
- Deepfakes in Financial Services: How AI Fraud Is Reshaping Risks in 2026, Fourthline
- Deepfake Statistics 2026: Growth, Fraud and Detection Data, StationX
- Deepfake Statistics 2026: Key Facts for CFOs, Eftsure
- Synthetic Identity Fraud and Deepfakes: Lessons from the 2026 Deepfake Summit, GetReal Security, June 2026
- Can Generative Models Actually Forge Realistic Identity Documents?, arXiv, 2026
- Why Your KYC Checks Are Failing Against AI-Generated Fraud, Fintech Global, September 2026
- Fintech: AI Regulation Must Be Grounded in Human Rights, International Bar Association, September 2026
- Financial Firms Operating in an AI Governance Vacuum, FOW, 2026
- Fintech Trends 2026, InnReg

Leave a Reply